Stop Patching by Panic:
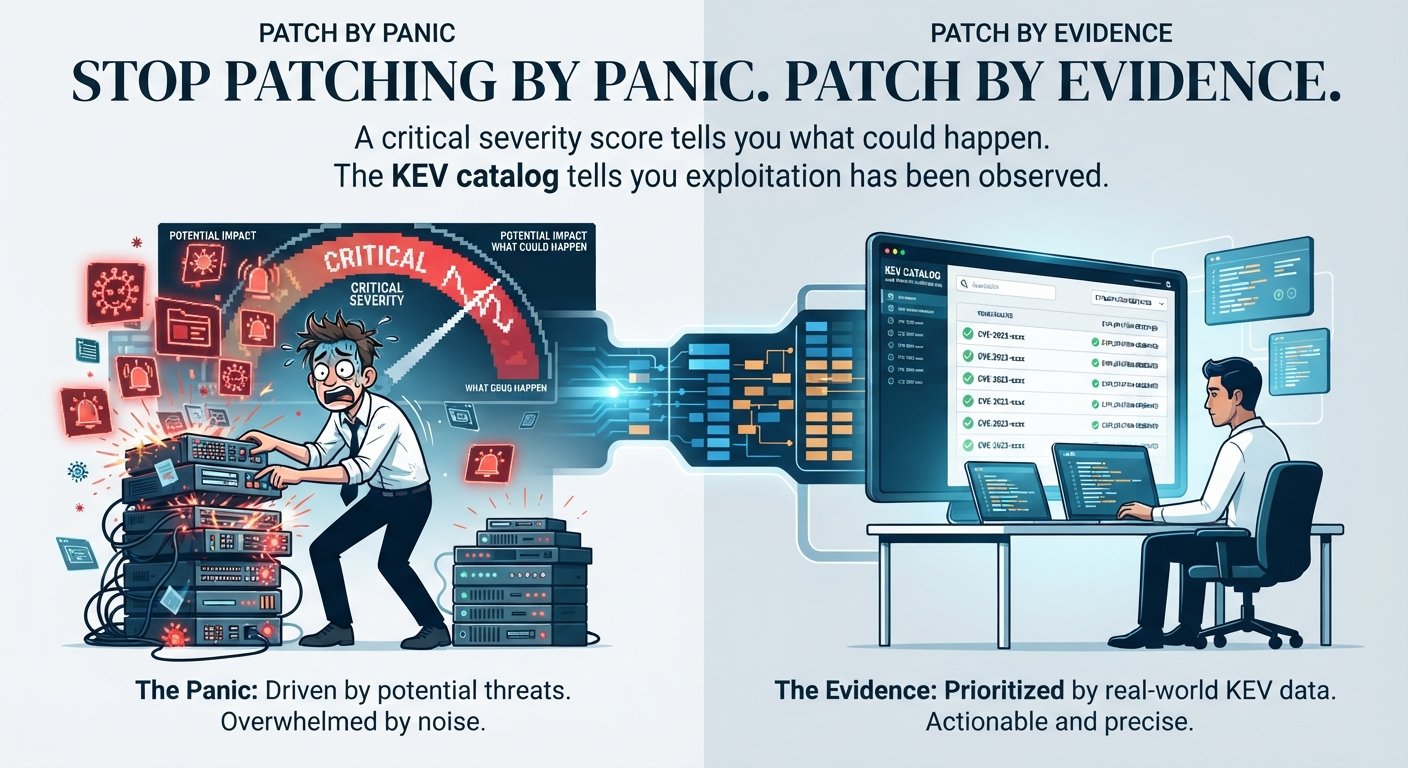
Stop patching by panic. Patch by evidence.
In August, CISA added actively exploited flaws affecting products including Microsoft SharePoint, VMware vCenter, Apple macOS, Oracle WebLogic components, and MLflow to its Known Exploited Vulnerabilities catalog.
A critical severity score tells you what could happen. The KEV catalog tells you exploitation has been observed.
Leadership should expect remediation to combine three facts:
Exploitation: Is the vulnerability being used in the wild?
Exposure: Is the affected asset reachable or accessible to likely attackers?
Business impact: What happens if that system is controlled or taken offline?
This week’s action: ask for one list—not three separate reports—showing KEV status, internet exposure, asset owner, business service, patch decision, and deadline.
The goal is not “patch everything immediately.” The goal is to move the risks most likely to become business incidents to the front of the queue.
#CISAKEV #VulnerabilityManagement #ThreatIntelligence #IndigoINT
Gunra Ransomware: The Two-Crisis Test for Executive Readiness
Ransomware is no longer one crisis. It is two.
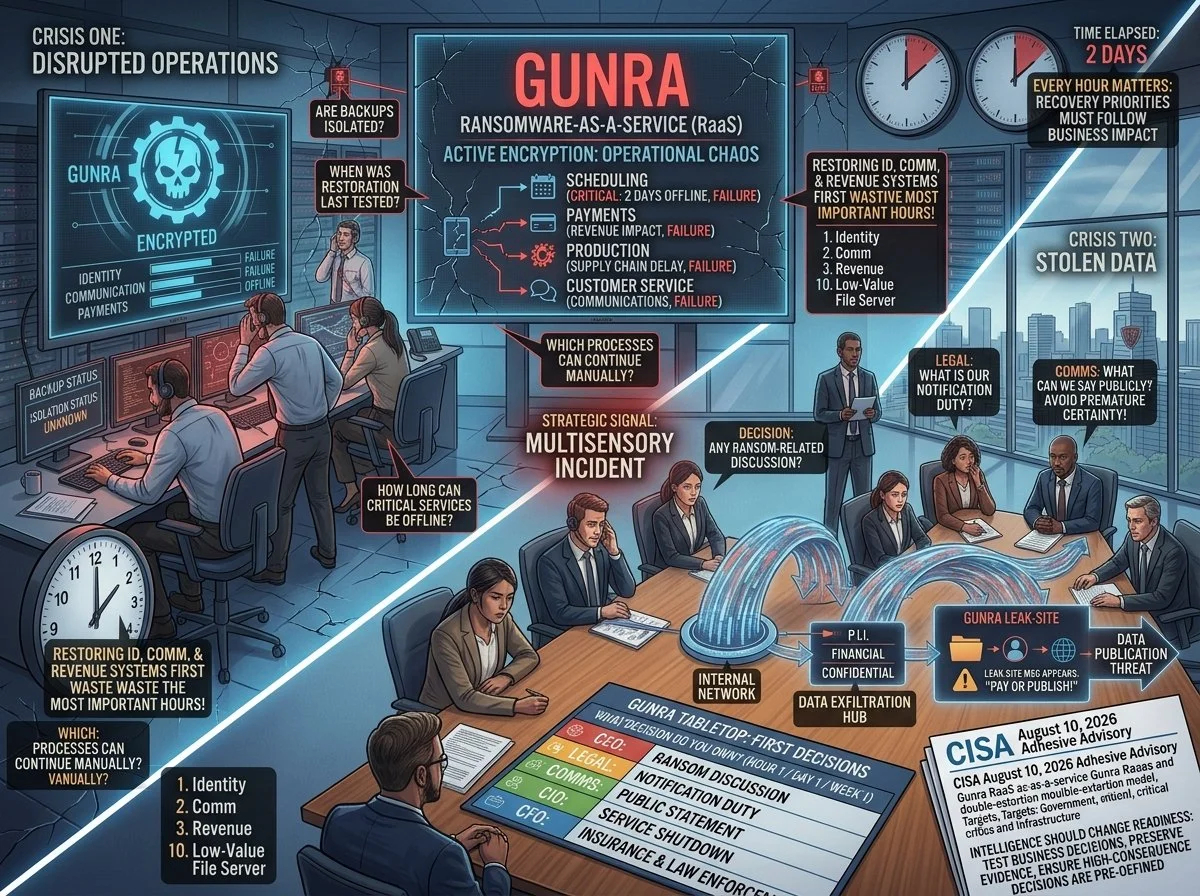
CISA’s August 2026 advisory on Gunra ransomware describes a ransomware-as-a-service operation using double extortion: encrypting systems while threatening to publish stolen data.
That creates two simultaneous executive problems:
Can we keep operating?
Can we manage the legal, customer, and reputational impact of stolen information?
A backup may help restore a server. It does not erase exfiltrated data, answer regulator questions, or tell customers what happened.
This week’s action: run a tabletop with one scenario—critical files are encrypted and evidence suggests customer data was copied. Require leaders to decide:
what gets isolated first;
which services continue manually;
who contacts counsel, insurance, law enforcement, and customers;
what evidence is preserved;
who has authority over ransom-related decisions.
The value of threat intelligence is preparation before pressure arrives.
#Ransomware #ThreatIntelligence #BusinessContinuity #IndigoINT
Trust Is the Attack Surface
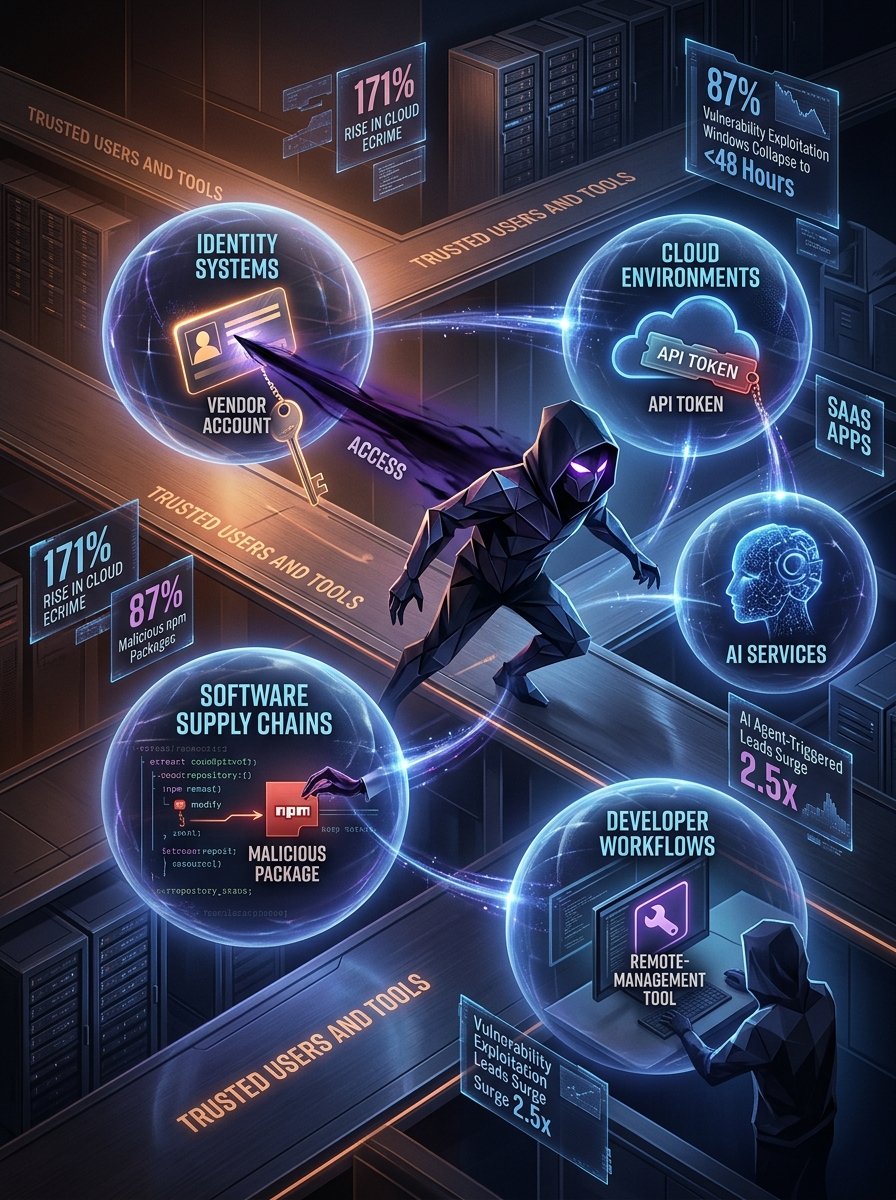
CrowdStrike’s 2026 Threat Hunting Report describes adversaries targeting trusted users and tools across identity systems, cloud environments, SaaS apps, AI services, software supply chains, and developer workflows.
This matters because “trusted” activity often receives less scrutiny. A vendor account, API token, remote-management tool, or developer credential may already have the access an attacker wants.
CYBER FRI — Phone systems, identity data & ransomware's supply chain toll
The Verizon 2026 DBIR found that 96% of ransomware victims are small and mid-size businesses. For executives, that's not a footnote — it's a supply chain risk. The same mid-market vendors you depend on for facilities, IT services, and logistics are the ones ransomware groups are targeting. An unpatched phone system at a vendor, a breach at a service provider, or a single ransomware incident in your supply chain can cascade into operational disruption, data exposure, and regulatory fallout. Threat intelligence programs that only track direct attacks on the enterprise are missing the larger attack surface.